5 guardrails before your AI agent touches live systems
5 guardrails before your AI agent touches live systems
Stop giving your agent write access on day one: Your CRM can change before anyone sees it.
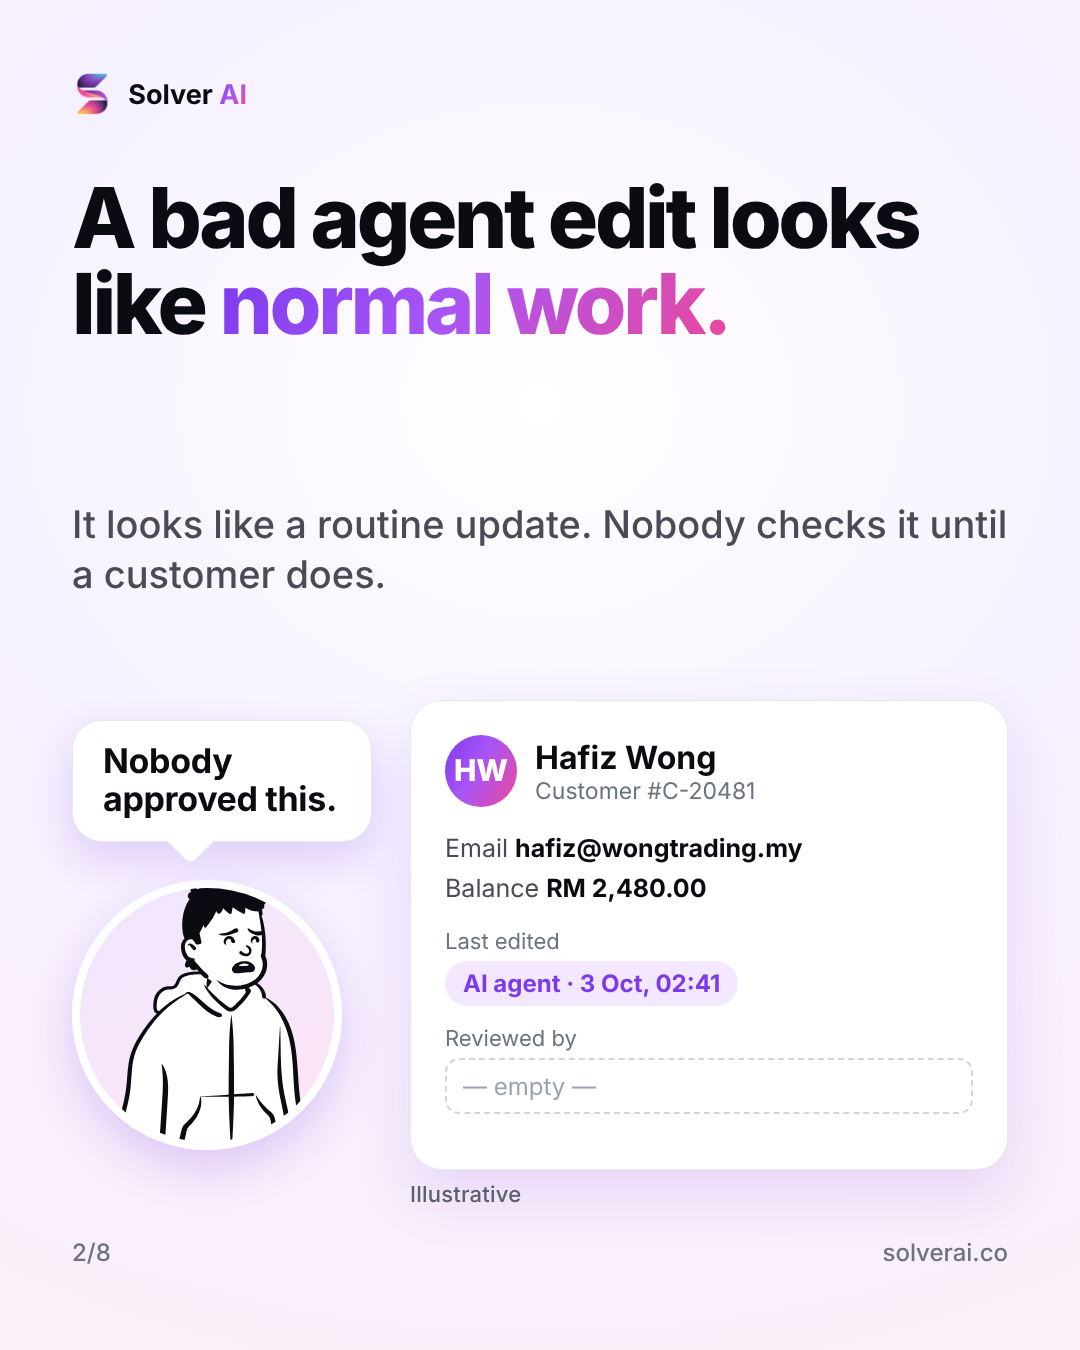
A bad agent edit looks like normal work: It looks like a routine update. Nobody checks it until a customer does.
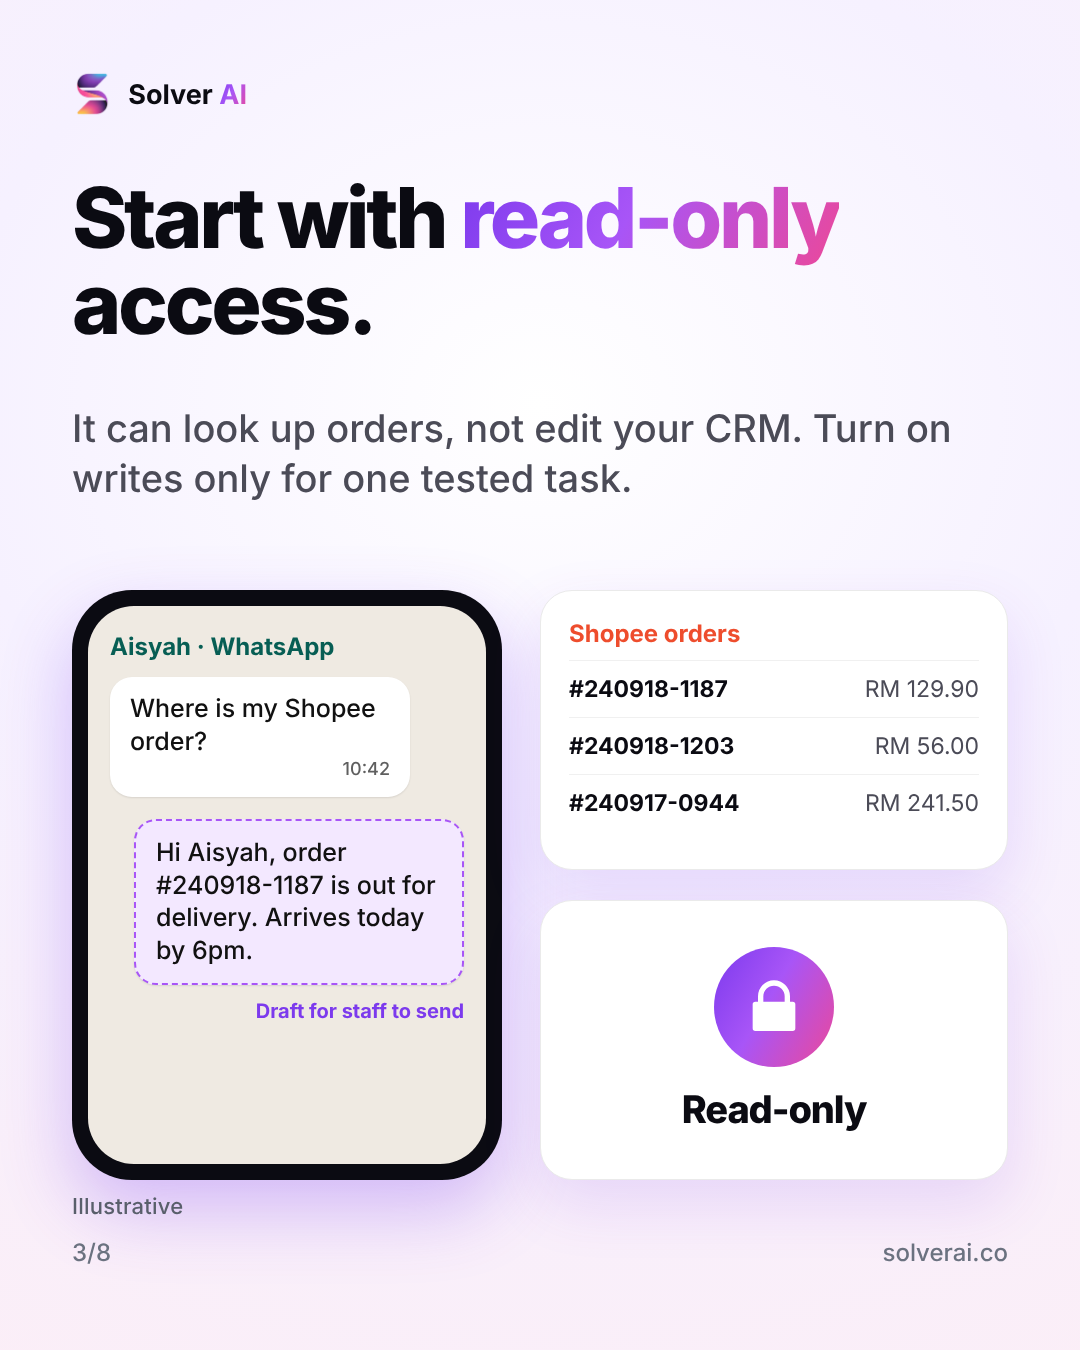
Start with read-only access: It can look up orders, not edit your CRM. Turn on writes only for one tested task.
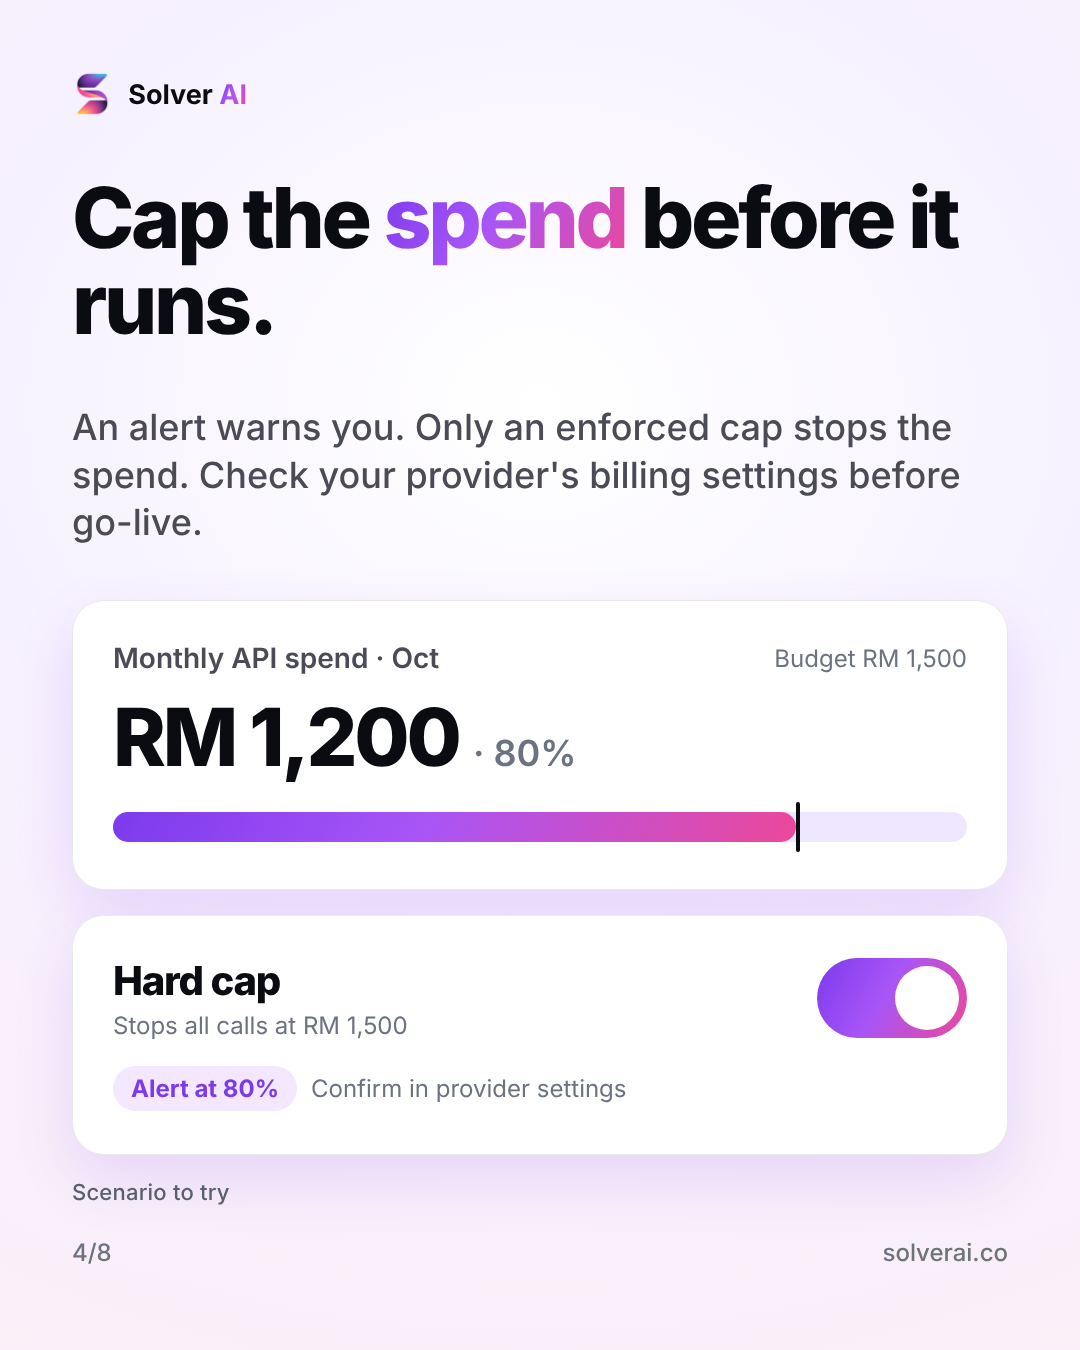
Cap the spend before it runs: An alert warns you. Only an enforced cap stops the spend. Check your provider's billing settings before go-live.
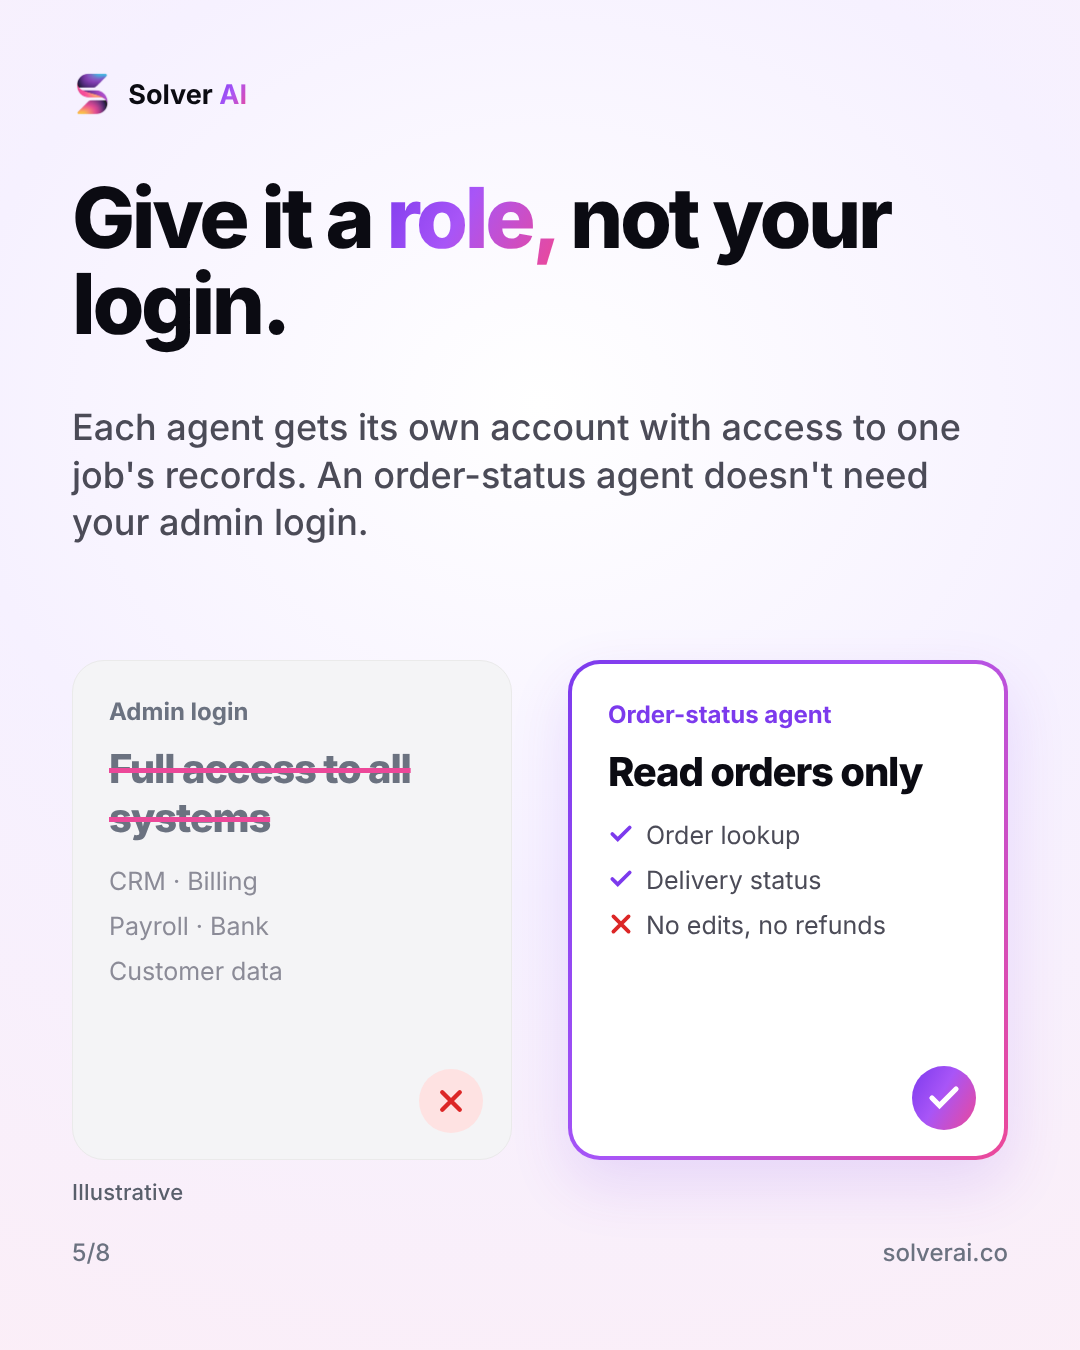
Give it a role, not your login: Each agent gets its own account with access to one job's records. An order-status agent doesn't need your admin login.
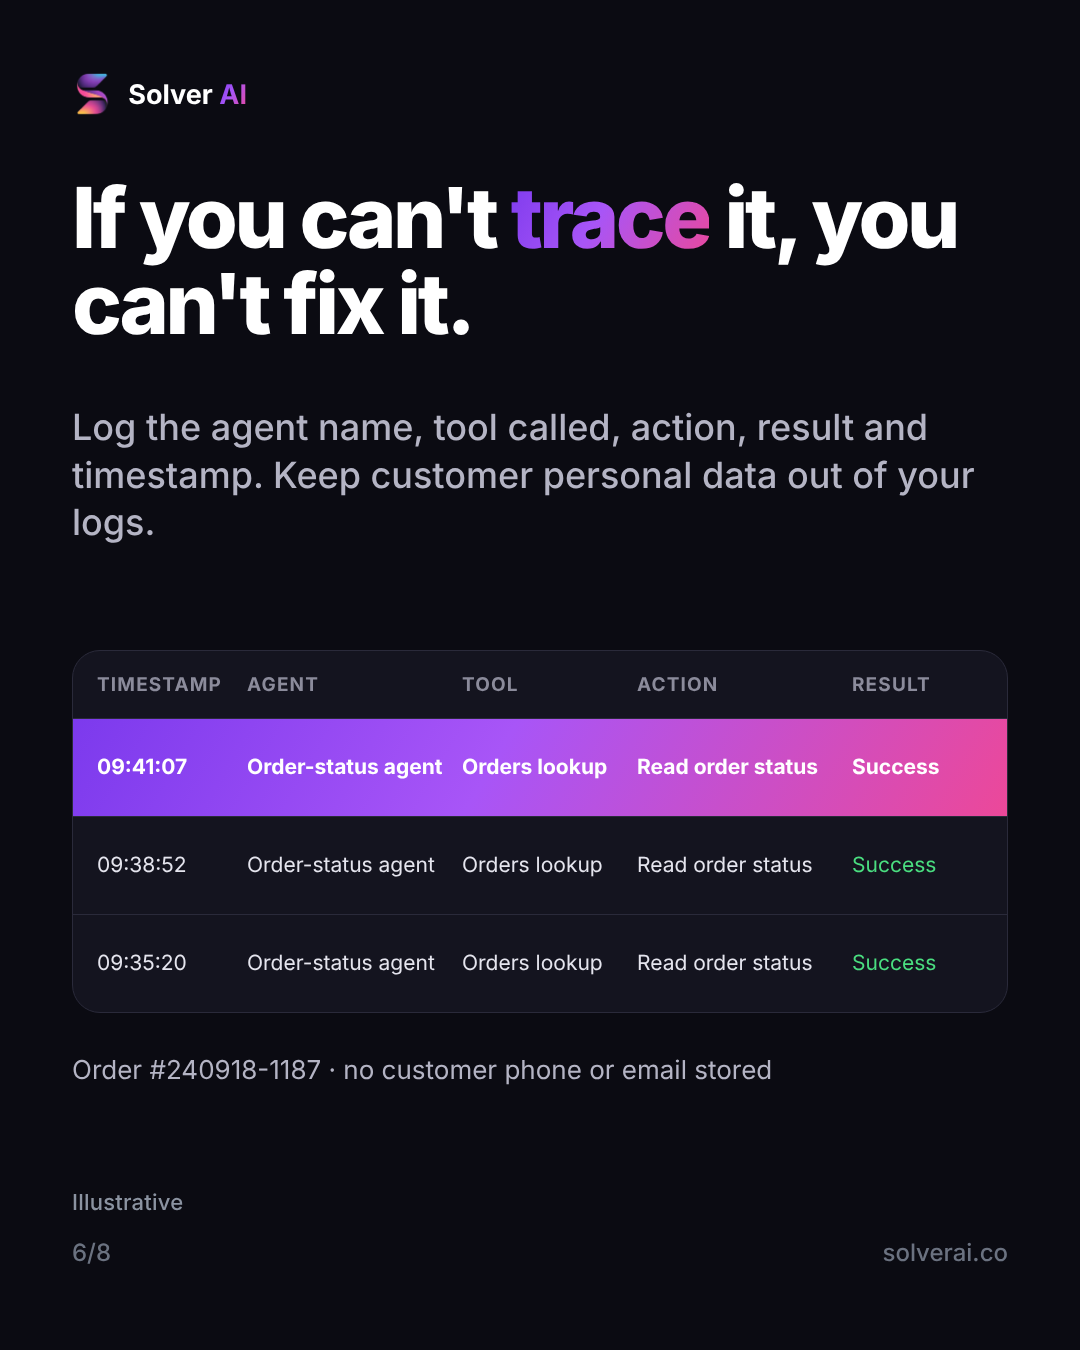
If you can't trace it, you can't fix it: Log the agent name, tool called, action, result and timestamp. Keep customer personal data out of your logs.
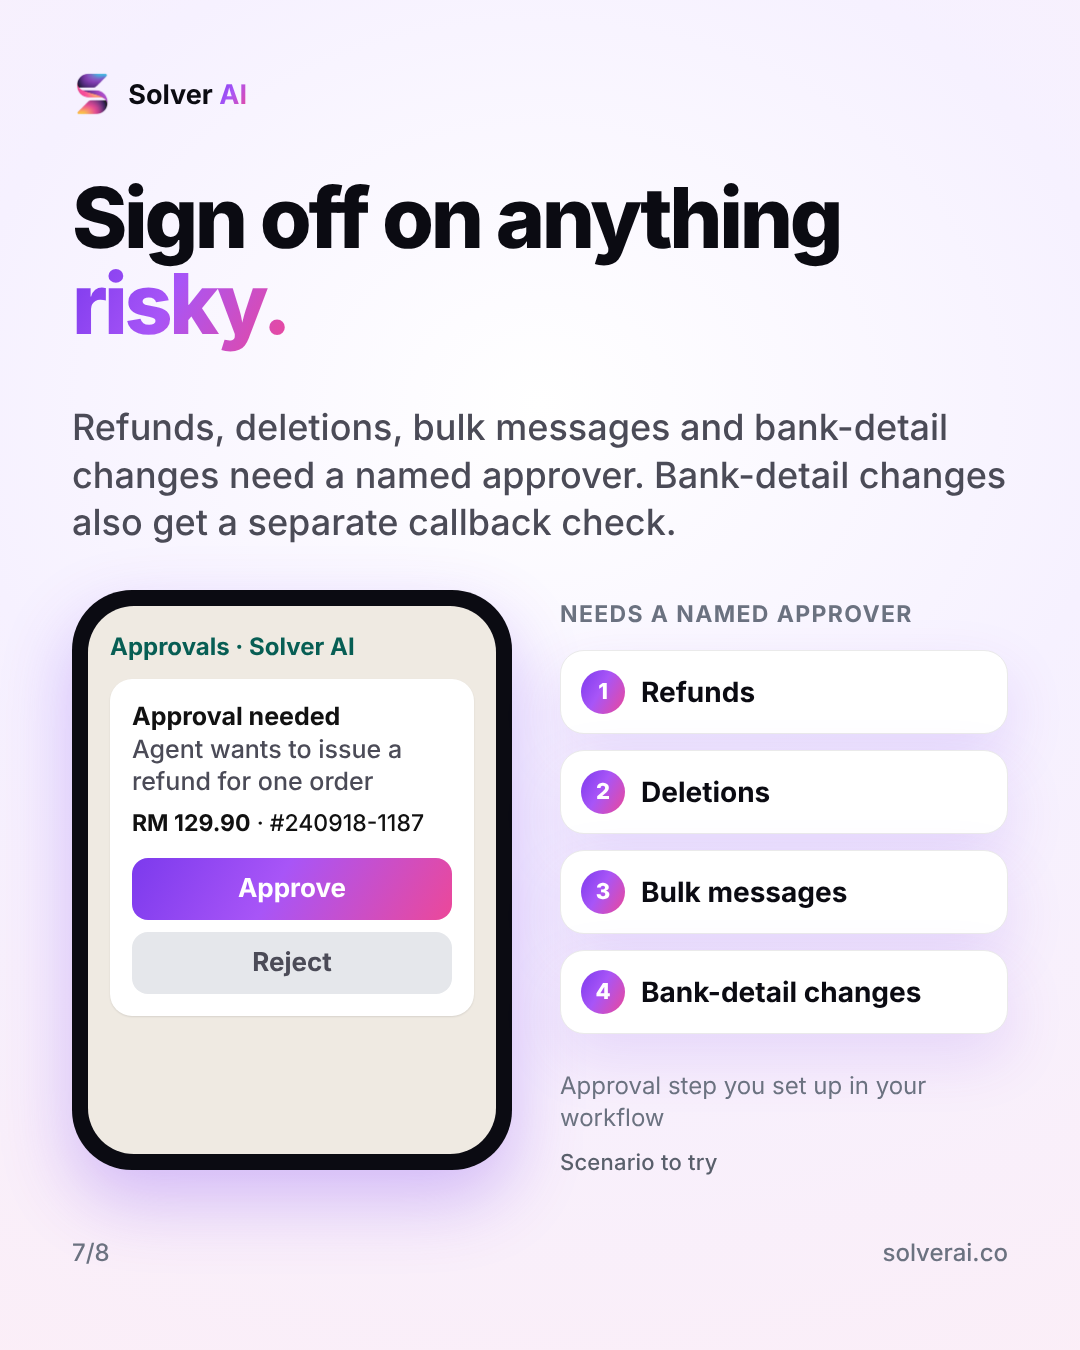
Sign off on anything risky: Refunds, deletions, bulk messages and bank-detail changes need a named approver. Bank-detail changes also get a separate callback check.
Send this to whoever sets up your AI tools: They'll want slide 3 before anything goes live.

Your AI agent can change your CRM before you see it. Here are five guardrails we'd set before any agent touches live systems: read-only access first, spend caps, a scoped role for each agent, audit logs and human sign-off on risky actions. Send this to whoever sets up your AI tools. Solver AI builds AI agents and workflow automation for Malaysian SMEs.

#AIagents #SMEMalaysia #AIgovernance #WorkflowAutomation #SolverAI

Want this running in your business?

Send this to whoever sets up your AI tools.